# COMPLYAN - Cybersecurity Compliance Automation Platform

Conquer Compliance, Deliver Assurance and Streamline Security

## What is Complyan?

Complyan is a comprehensive, all-in-one SaaS Governance, Risk & Compliance (GRC) platform focused on cybersecurity and data protection. It offers modules for:

* Cybersecurity Compliance (e.g ISO 27001, NIST CSF, PCI-DSS, GDPR)
* Third-party/vendor risk management
* Internal and external audit process
* Data privacy, flow-mapping and repoting

Its goal is to centralize compliance workflows, automate evidence collection, map controls across frameworks and offer real-time dashboards.

## **Mission**&#x20;

At Complyan, our mission is to empower organizations to effectively manage their cybersecurity and data privacy risks, ensuring compliance with relevant regulations and standards. We strive to provide a comprehensive and intuitive platform that helps organizations to efficiently and effectively assess, mitigate, and report on their compliance activities.

## **Vision**&#x20;

Our vision is to be the leading provider of cybersecurity governance, risk management, and data privacy solutions, enabling organizations around the world to confidently navigate the complex landscape of regulatory requirements and best practices. We aim to help organizations of all sizes to protect their sensitive data and ensure the privacy of their customers or users, ultimately building trust and enabling them to succeed in the digital age.

## Key Features

* **Framework Marketplace & Cross-Mapping**: Supports 30+ standards (global, regional, sector-specific). Encourages re-use through linked control libraries.
* **Automated Evidence & Continuous Monitoring**: Integrates with Azure, AWS, Office 365, Okta, Nessus, Qualys, etc. for automatic evidence collection and ongoing compliance checks
* **Risk and Audit Management**: Tools for compliance risk assessments, internal/external audits, real‑time gap analysis, dashboards, and templated reports
* **Third-Party & Vendor Risk Module**: Enables vendor self‑assessments, questionnaires, risk scoring, and continuous tracking
* **Data privacy & Governance Support**: Covers data mapping, privacy impact assessments, and compliance with GDPR and similar regulations
* **Compliance Wizard**:
  * Simplifies the compliance process by guiding users through control setup and implementation.
  * Allows users to **add control custodians**, maturity levels, and implementation details.
  * Automates compliance workflows, saving time and effort for compliance teams.

## Who Should Use This Manual

This manual is designed for:

* **Compliance Officers & CISOs** – Managing cybersecurity and data‑privacy standards.
* **IT Risk & Security Teams** – Performing risk assessments and monitoring controls.
* **Audit & Legal Professionals** – Planning internal/external audits and compiling documentation.
* **Vendor/Procurement Managers** – Overseeing third‑party risk and vendor compliance.
* **Executives and Board Members** – Tracking compliance progress via dashboards and reports


# Getting Started

To use Complyan effectively, ensure your environment meets the following requirements:

***

### **Supported Browsers**

* Google Chrome (latest version)
* Microsoft Edge (latest version)
* Safari 15 and above (macOS)

### **Network**

* Stable internet connection (minimum 10 Mbps recommended)
* Firewall access allowing HTTPS traffic to complyan.com and associated subdomains


# How to Sign Up/Sign In

## Signing Up

***

Navigate to https//app.complyan.com. A business domain (not Gmail, Yahoo! etc.,) is required to sign up.

Select **Sign Up & Organization**

<figure><img src="https://1429514262-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FHUSn1rDjbkZnTYOhEpPG%2Fuploads%2F6JIUFlPdufgV9itPvNpR%2Fimage.png?alt=media&amp;token=f1238221-167d-4709-865a-723d362d3e77" alt=""><figcaption></figcaption></figure>

***

Note: Read through **Privacy Policy** and **Terms & Conditions** before accepting and proceeding.

<div align="left"><figure><img src="https://1429514262-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FHUSn1rDjbkZnTYOhEpPG%2Fuploads%2FLcrQiFaaZN1nBzVnqUU4%2Fimage.png?alt=media&amp;token=c1ff88d2-739c-4399-a8f1-40e794fb50d1" alt="" width="316"><figcaption></figcaption></figure> <figure><img src="https://1429514262-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FHUSn1rDjbkZnTYOhEpPG%2Fuploads%2FBqDvJm7XxP84MsDDl4H2%2Fimage.png?alt=media&amp;token=bdf6d0d6-3ddd-4946-afc0-b8c2b35f431d" alt="" width="306"><figcaption></figcaption></figure></div>

***

## Signing In

Return to [www.complyan.com](http://www.complyan.com) and **Sign In** with the registered credentials from the **Sign Up** process.

<figure><img src="https://1429514262-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FHUSn1rDjbkZnTYOhEpPG%2Fuploads%2FtZZwhLmxsc2ihghaLXxy%2Fimage.png?alt=media&amp;token=0cd0187b-92e8-4fa3-b2fd-1c7e1aed1899" alt=""><figcaption></figcaption></figure>


# Navigating the Dashboard

Once logged in, the main Complyan Dashboard will be in view.&#x20;

***

Toggle between frameworks by clicking the highlighted box. This dashboard gives an overview of all modules and the progress levels across them.

<figure><img src="https://1429514262-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FHUSn1rDjbkZnTYOhEpPG%2Fuploads%2FmPfOd3qSvFiISbrzH8T2%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%208.png?alt=media&amp;token=b0c16072-a31b-4bfc-be04-72005123d435" alt=""><figcaption></figcaption></figure>

***

Use **Manage Charts Visibility** to customize the look and feel of your dashboard

<figure><img src="https://1429514262-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FHUSn1rDjbkZnTYOhEpPG%2Fuploads%2FpnYhOyMVbTS30Hql2l8j%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%209.png?alt=media&amp;token=3862a408-d8ab-4bc4-8ca4-18a520c8abca" alt=""><figcaption></figcaption></figure>

***

The dashboard may also be exported by clicking the highlighted icon at the top right corner.

<figure><img src="https://1429514262-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FHUSn1rDjbkZnTYOhEpPG%2Fuploads%2FNUo9lk1AChnvxxh7cfRc%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2011.png?alt=media&amp;token=d26ab4a9-6a78-433e-a35a-f1acd51379d5" alt=""><figcaption></figcaption></figure>

***


# AI Usage Disclaimer

#### **1. General Information**

ComplyBot is an Artificial Intelligence (AI)-powered assistant designed to support users with information related to governance, risk management, compliance, and associated domains.

The system generates responses based on patterns in data and does not possess human judgment or independent reasoning.

***

#### **2. No Professional Advice**

Responses provided by ComplyBot are for **informational and assistive purposes only** and do not constitute:

* Legal advice
* Regulatory advice
* Audit opinions
* Professional consulting services

Users must **exercise independent judgment** and consult qualified professionals before making decisions based on system outputs.

***

#### **3. Accuracy and Limitations**

While reasonable efforts are made to ensure the reliability of outputs:

* Responses may be **incomplete, outdated, or inaccurate**
* The system may generate **plausible but incorrect information (hallucinations)**
* Contextual misunderstandings may occur

Users are responsible for **validating outputs** before use in decision-making or operational processes.

***

#### **4. Human Oversight Requirement**

ComplyBot is not a substitute for human expertise.

All outputs should be:

* Reviewed by appropriate personnel
* Verified against authoritative sources
* Subject to organizational approval processes where required

***

#### **5. Data Usage and Privacy**

Users must not input:

* Personal data unless explicitly authorized
* Sensitive or confidential information without proper classification and controls
* Regulated data unless permitted by organizational policy

Any data entered into ComplyBot may be processed in accordance with applicable data protection laws and organizational policies.

***

#### **6. Security and Acceptable Use**

Users shall not:

* Use ComplyBot for malicious, unlawful, or unauthorized purposes
* Attempt to manipulate, exploit, or bypass system safeguards
* Input harmful code, prompts, or instructions intended to degrade system integrity

All usage is subject to monitoring and may be logged for security and compliance purposes.

***

#### **7. Bias and Fairness Notice**

AI-generated outputs may reflect:

* Biases present in training data
* Limitations in model design

The organization implements controls to monitor and mitigate bias; however, users should remain aware of potential limitations and report any suspected bias.

***

#### **8. Availability and Performance**

The system is provided on an “as available” basis.

The organization does not guarantee:

* Continuous availability
* Error-free operation
* Performance consistency under all conditions

***

#### **9. Liability Limitation**

The organization shall not be liable for:

* Decisions made based on AI-generated outputs
* Any direct or indirect losses arising from system use
* Misinterpretation or misuse of responses

Use of ComplyBot is at the user’s own risk.

***

#### **10. Continuous Improvement**

ComplyBot is subject to ongoing monitoring and improvement.

Outputs and system behavior may change over time as part of:

* Model updates
* Risk mitigation efforts
* Performance enhancements

***

#### **11. User Acknowledgment**

By using Complyan users acknowledge that they:

* Understand the capabilities and limitations of its AI system
* Accept responsibility for validating outputs
* Agree to comply with applicable policies and guidelines

***

> *ComplyBot is an AI-powered assistant providing informational support only. Outputs may be inaccurate or incomplete and must be independently verified. Do not input sensitive or personal data unless authorized. Use is subject to monitoring and applicable policies.*&#x20;

***

#### **12. Reporting AI Issues and Adverse Impacts**

The organization is committed to the responsible and safe use of Artificial Intelligence systems. Users and other interested parties are encouraged to report any concerns, issues, or adverse impacts arising from the use of ComplyBot.

Examples of reportable issues include, but are not limited to:

* Inaccurate, misleading, or harmful outputs
* Suspected bias or unfair treatment
* Security vulnerabilities or data exposure risks
* Inappropriate or unsafe system behavior
* Any unintended consequences impacting users or stakeholders

#### **How to Report**

Reports can be submitted through the following channels:

* **Email:** `security@complyan.com`

When submitting a report, please include (where possible):

* Description of the issue
* Date and time of occurrence
* Relevant input and system response
* Any supporting evidence (e.g., screenshots)

#### **Handling of Reports**

All reported issues will be:

* Logged and assessed in accordance with internal procedures
* Reviewed by appropriate personnel
* Investigated and addressed based on severity and impact

The organization will take appropriate corrective actions where necessary and may use reported information to improve system performance, safety, and governance.<br>


# Marketplace

All standards and regulatory compliance frameworks available on Complyan are visible here.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FxX4Ds9TCHpP9elsNUFmt%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2019.png?alt=media&amp;token=63c2484e-4a6f-4a79-89da-a381d9335b32" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FRzkNujDadZNjn98nI1gT%2Fimage.png?alt=media&amp;token=c20a44b9-e109-44ff-84d7-592f72f47053" alt=""><figcaption></figcaption></figure>

Use the **Search** functions to look up global, international and local frameworks.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FYfUYCnyojJzoqcirNU3S%2Fimage.png?alt=media&amp;token=4ac52dfc-8819-4fea-8ea2-040c0570fbf4" alt=""><figcaption></figcaption></figure>

***

To subscribe:

* Find a framework of choice either by browsing or searching for it
* Select View Details on chosen framework

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FLAMBeC1dqfYsBMkZEiSz%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2025.png?alt=media&amp;token=84ba4775-972d-498a-a4b4-579ca2ba89d8" alt=""><figcaption></figcaption></figure>

* Click Subscribe

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FzohKfK2Bx7rb1W2sPnU8%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2026.png?alt=media&amp;token=cf3cf878-2412-4718-b078-305676182472" alt=""><figcaption></figcaption></figure>


# My Frameworks

This is the library for all frameworks you have successfully subscribed to.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FmcSX7V8Ird0gVHB1DsLQ%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2020.png?alt=media&amp;token=c086b620-44d1-4159-8aea-0c078b0dcebd" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F3Aty5UiR2BAT7Emw2AsP%2Fimage.png?alt=media&amp;token=148d0c4a-3c81-496a-900e-2c09c19ebf8f" alt=""><figcaption></figcaption></figure>


# Implementing Controls

To view all controls and sub-controls under a framework and proceed to implementation:

* Select **Preview Controls** to see all controls specific to a domain.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2Fp559Unbijn4xZra91JeY%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2030.png?alt=media&amp;token=0a9c63ef-de52-4d23-ad22-02c7562aebca" alt=""><figcaption></figcaption></figure>

* Or use **View Controls** to see controls across all domain and select **Report** to export a consolidated document of control information.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FXownAD4EFbd5qgj65oki%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2034.png?alt=media&amp;token=b6eb0f30-ec1e-486a-8e6b-d53a657e3044" alt=""><figcaption></figcaption></figure>

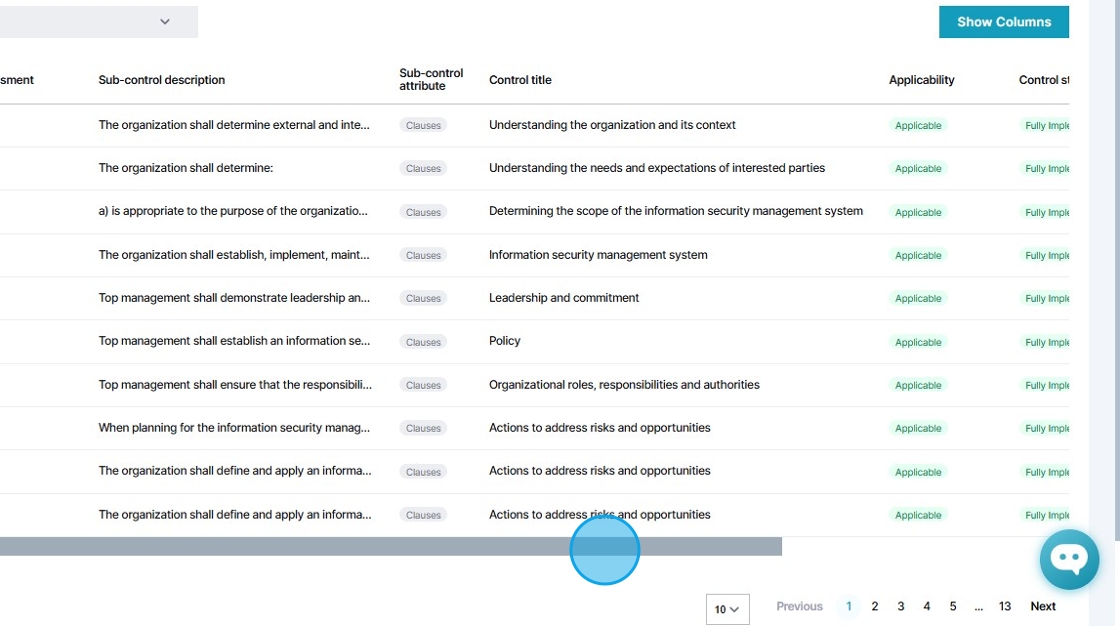
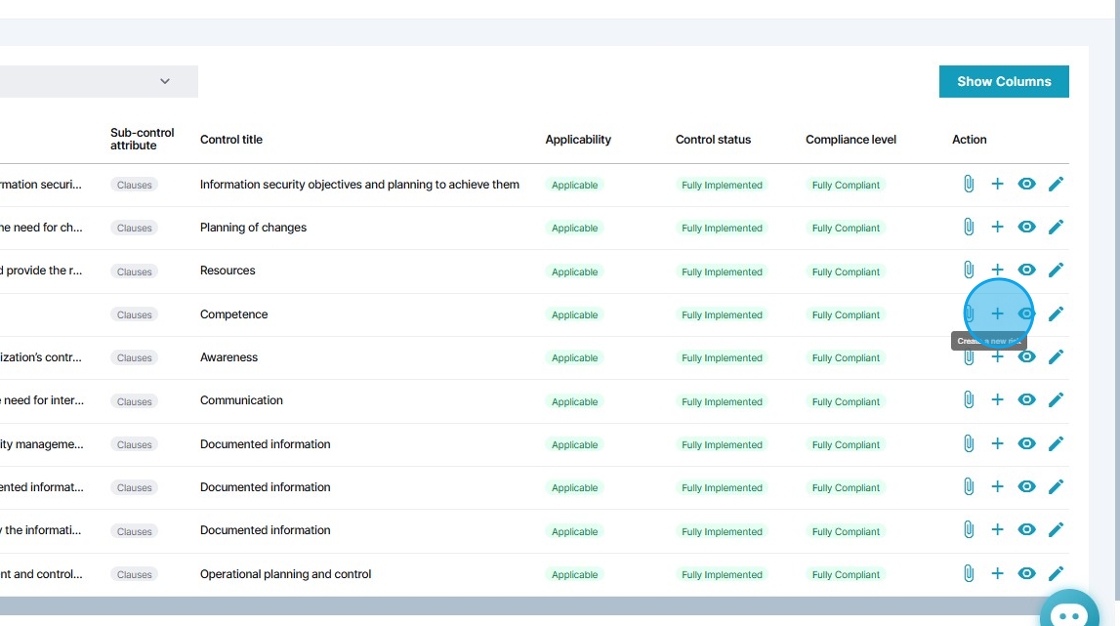
* Move the slider to reveal action buttons at the end of each control.

<div align="left"><figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F3UFlN7Sr1xOTR2xWlZYw%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2035.png?alt=media&amp;token=3f3eb14b-052a-49d8-84c8-3aa4bab39bf0" alt=""><figcaption></figcaption></figure> <figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F3VC6HdnKjN2fB1sohQx9%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2036.png?alt=media&amp;token=84f1396b-5383-45b4-b33f-cde1161c65c4" alt=""><figcaption></figcaption></figure></div>

* Select **Edit** to begin.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FlCZWN9BcAjhQ1VCb5Wea%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2039.png?alt=media&amp;token=3ee7f865-44a6-4297-b223-53b0a4bdad22" alt=""><figcaption></figcaption></figure>

* Determine whether the control is relevant to your organization and select **Applicable** or **Not Applicable** and proceed.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FXOvfgPaVT8AuFeKYK6WW%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2040.png?alt=media&amp;token=d35930f7-db3d-4558-b900-f70c688baca7" alt=""><figcaption></figcaption></figure>

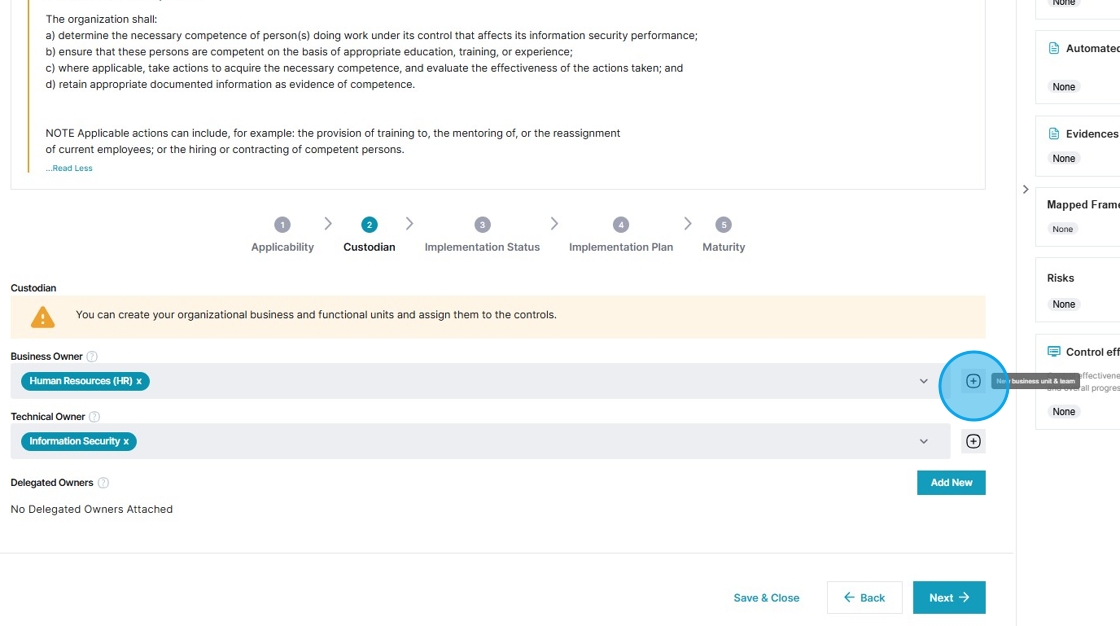
* Select custodians for the control under **Business Owner** and **Technical Owner**. Click on the highlighted button to create new business units.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F7tTTNA2bSGrvTkP2cR0x%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2042.png?alt=media&amp;token=53f7505a-cb9f-4624-adee-c659cd5e4d8f" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FvnG1nPqRV1lscLk8yZWa%2FScreenshot%202025-07-17%20125853.png?alt=media&amp;token=309eb53d-3314-46ff-8120-d9f1259e75c8" alt=""><figcaption></figcaption></figure>

* Toggle the RUN switch on top of the control implementation pane to use Complyan's AI feature in filling out details.\
  \
  ![](https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F7NPFNnAfDvZJUOhP4Wpp%2Fimage.png?alt=media\&token=d498e34a-e4de-41b6-be87-61cda27d3e3f)<br>
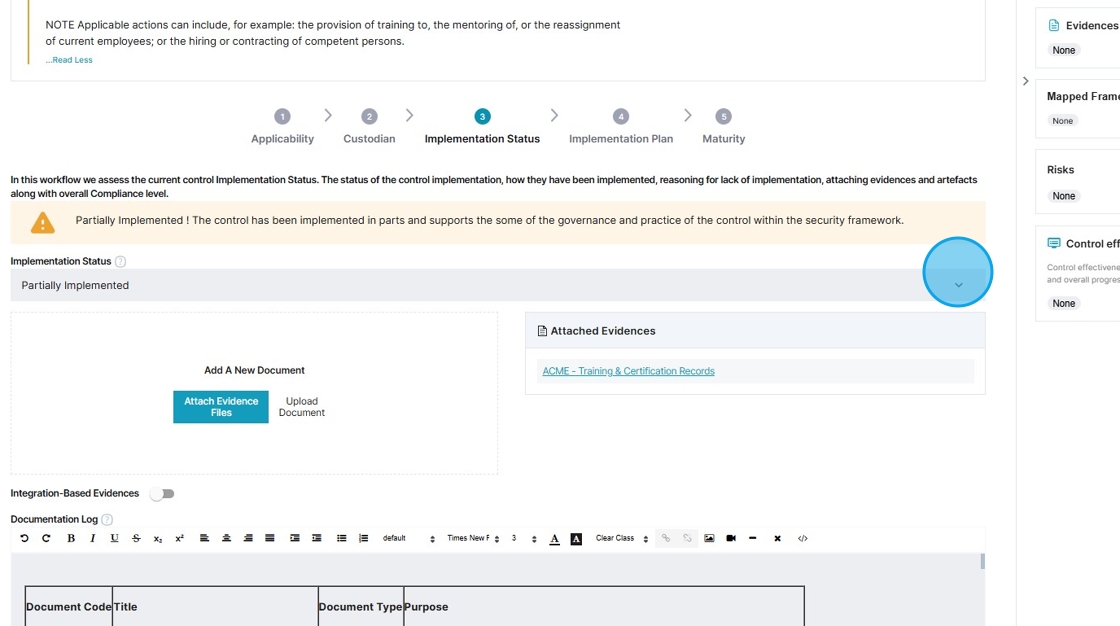
* Click to select **Implementation Status.**

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F2VmZxO17sdBP09QmtmlD%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2048.png?alt=media&amp;token=17c54bf7-1899-4ff1-8d31-6a36bfe4bbba" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2Fq3JZidNlvjGZ9uesdlzL%2Fimage.png?alt=media&amp;token=4b6f81d0-20da-4a0e-84f9-e75ace2affd2" alt=""><figcaption></figcaption></figure>

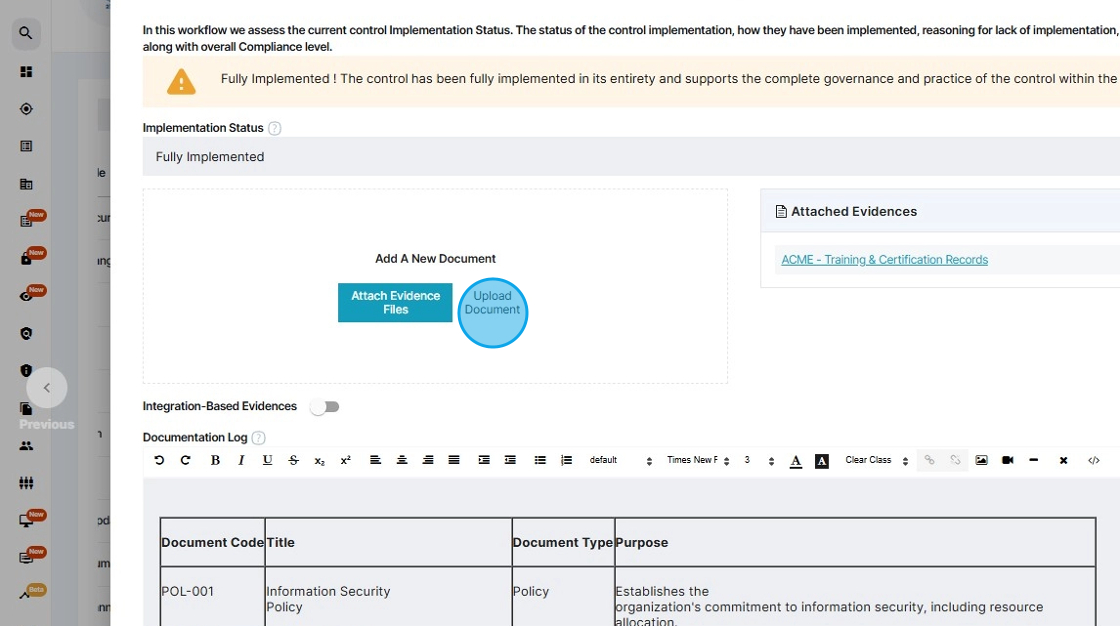
* Attach evidence of implementation by uploading or selecting from files you have previously uploaded.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FXtPKNjwXjfF6ktVUKDAr%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2074.png?alt=media&amp;token=70757fd3-fdaa-4d96-a9f1-b8c932ac8d09" alt=""><figcaption></figcaption></figure>

* Enter a list of documents relevant to the implementation of the control. Extend the size of the text box by using the arrow at the highlighted edge.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FbitKyReH1fdE6WdgLkkP%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2050.png?alt=media&amp;token=d0624ec3-5ef0-4a91-9f85-abb2c448126c" alt=""><figcaption></figcaption></figure>

* Enter details of implementation of this control in your organization.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FEoTuutXQUpRUfbT6YKFm%2Fimage.png?alt=media&amp;token=7ff44c70-3356-488d-95fe-6305de35ac9f" alt=""><figcaption></figcaption></figure>

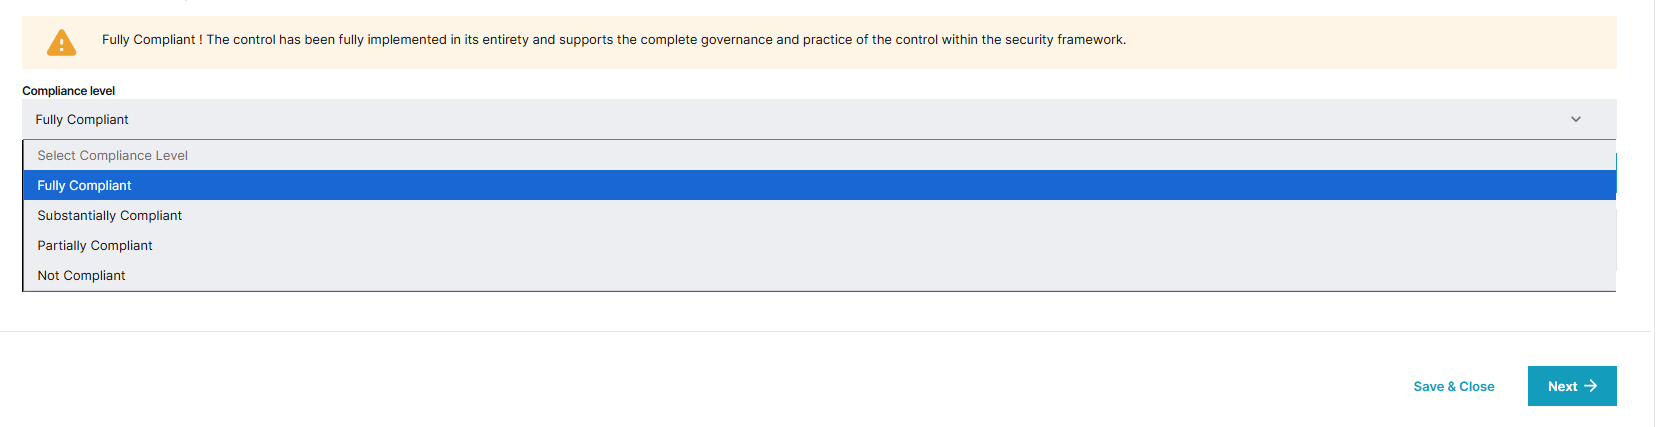
* Select **Compliance Level.**

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FVogg0as5Cd95bwt0wPQo%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2057.png?alt=media&amp;token=bf141381-367b-47bb-8b87-8ff722022053" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FcRU9DdPaembsJqBh2asR%2Fimage.png?alt=media&amp;token=5f15ef4c-5c3b-41bc-aaaf-29e4b49a414f" alt=""><figcaption></figcaption></figure>

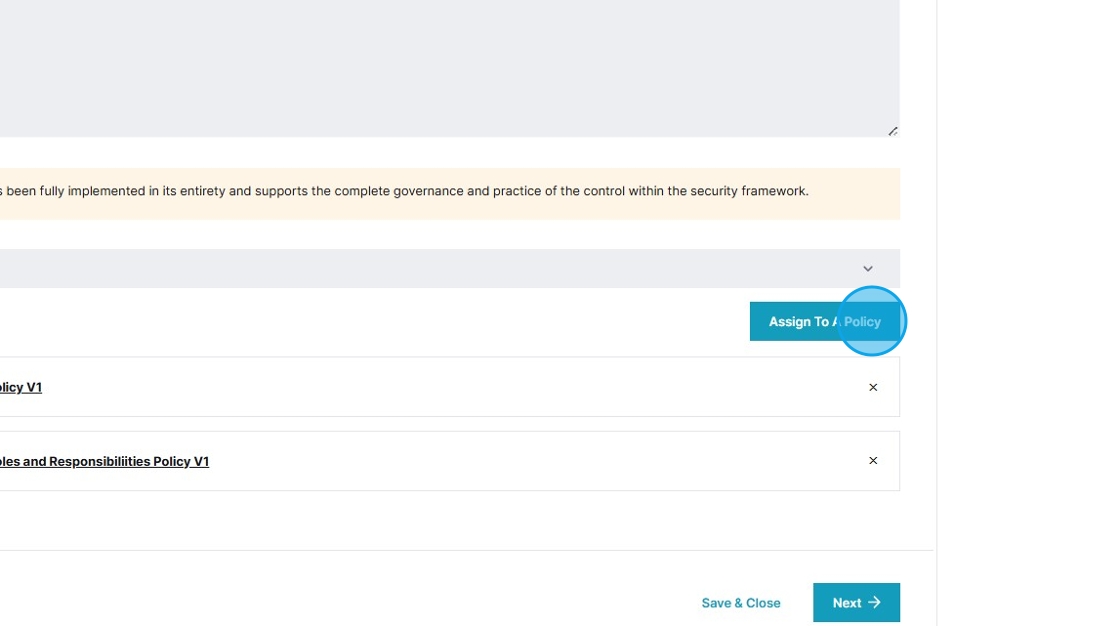
* Optionally, you can assign the control to a policy by selecting **Assign To A Policy**.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2Fv5LPwPWiLxJNYzoIwsUr%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2058.png?alt=media&amp;token=327a1f7f-5216-46fd-81b3-b8baa9c32e48" alt=""><figcaption></figcaption></figure>

* If any selection is made other than **Fully Implemented**, you will be required to enter a plan to meet full implementation.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F8ZnvNOjiL4hsICkHVodv%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2063.png?alt=media&amp;token=55e212b2-7627-422b-9b49-99298fa26731" alt=""><figcaption></figcaption></figure>

* Finally, select maturity at **Governance** & **Technical** levels and select **Submit**.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FGJzc4yUSAYulBaGYons8%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2070.png?alt=media&amp;token=031dd13c-66ce-4363-99e4-336a1ad4ada1" alt=""><figcaption></figcaption></figure>

* Use the highlighted action button to preview all details you have entered.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FIq6Q12iwdAEwzNot6Ezw%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2078.png?alt=media&amp;token=6823bb07-aee5-42df-a85e-afe17ea31534" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F5EVDV4XNAnSpcYd7C5n6%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2081.png?alt=media&amp;token=7fdf33a2-7208-4b0b-945f-cb7c065865f9" alt=""><figcaption></figcaption></figure>

* You can also leave comments in this section.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FDuhW0zmtjGF9wbAV4EQl%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2088.png?alt=media&amp;token=542b0378-4a8e-4003-ad8d-23a50e1c2b84" alt=""><figcaption></figcaption></figure>

* Select the highlighted icon to link control to an existing risk

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FiLzVgvH049ZmmFGiuKhm%2FManaging%20Compliance%20Frameworks%20in%20Complyan%20-%20Step%2090.png?alt=media&amp;token=432e75e4-3cd7-44cd-9303-4a0deed27dfd" alt=""><figcaption></figcaption></figure>


# Unified Complyan Controls


# Overview of the UCC Dashboard


# How To Edit Base Framework Settings


# Generating A Base Framework Report


# Policy Management


# Accessing All Policies

This interface displays all policies which have been created and used across frameworks.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXdY70M1rhGBz7WBYN0wYnIEXbIzbqo7nqxQm_FdY49MH9ycruTvgkd5xxHrW_IcIHOVmWYFvRWP7-j9oNtuPzeK1jvw-qQs7r-fJPwqRHvGxRT0bPtyeQa3Q8Rc2V0cO40GBrAoqVVDUpCXC8zOaUdKvvAc?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>


# Creating A New Policy

To create a new policy, click on **Create New Policy**. Input the name of the policy and add a short description with details such as version number (v1.0, v2.0 etc.). Optionally, the policy can be attached to a control by selecting **Attach Framework.**

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FmAzLbupfCLnzdiIMs01U%2FCreate%20a%20New%20Policy%20in%20Complyan%20-%20Step%204.png?alt=media&amp;token=1e5dd82f-4faa-421f-9743-ab76a89b4363" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FQGruKEgS1l22B7Ht5Lzz%2FCreate%20a%20New%20Policy%20in%20Complyan%20-%20Step%205.png?alt=media&amp;token=431f8f31-f16f-425f-b82a-d9c7ca1cdb18" alt=""><figcaption></figcaption></figure>

After this, a new policy will be created as a placeholder. To finish, click on **Start.**

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FxXMsqMNEbsjJE86M7Dyv%2FCreate%20a%20New%20Policy%20in%20Complyan%20-%20Step%2010.png?alt=media&amp;token=ff59752c-6ec9-4780-a06f-42db9eea2b14" alt=""><figcaption></figcaption></figure>

Select between creating one using Complyan's templates or uploading an already existing file. Note, different types of documents; policies, procedures, processes, guidelines etc., can be uploaded in this module.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F5Vgl1Xcaqw6pbNN7Qsbg%2FCreate%20a%20New%20Policy%20in%20Complyan%20-%20Step%2011.png?alt=media&amp;token=f216dced-5ef1-4bc8-96a6-aa0a9159c632" alt=""><figcaption></figcaption></figure>

Follow steps after selecting your preferred method to complete the creation of a new document.

To view inbuilt policies and documents on Complyan or only see documents created by you, toggle the highlighted button.

<div><figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FZ8icqGbQlLGX99bv8GYB%2FCreate%20a%20New%20Policy%20in%20Complyan%20-%20Step%203.png?alt=media&amp;token=b445adc3-d287-4407-8aa0-4002fd176dfe" alt=""><figcaption></figcaption></figure> <figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F13Qv3TpMHA4nUmCVlxh4%2FCreate%20a%20New%20Policy%20in%20Complyan%20-%20Step%202.png?alt=media&amp;token=a958ceb0-c648-4727-a941-e4a3aa3f56f8" alt=""><figcaption></figcaption></figure></div>


# Policy Knowledge Base

This displays not just policies but procedures, standards, plans, checklists etc regardless of what frameworks or controls they are attached to.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXchnO4hYrHpYwGNa6em9qBHF0K5U3N3las-7tR-Y-6USgjVF6z6Sjr7fXdHHkn4qtaFAYL_NXkzn8y8JtK0O6ut83j1C6IWsZRmim5nZL4YvxnaXnq_bo2NW_fv5cLcI3BLHcLh2bYq-05CyVSh5zISSNYJ?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXf8x9AbOc4QO-203BV_A_XeznkFQN2MfYLhIEXeTAtf_CLAAv8AqL5DfOZ-RVIZO78hAnIlu_b-7DRoVn2x0-ZOlcLh0yF_bN-fxnUzHENk6Qbt0ChDKiCjuHSvALn67tXHQ48jxFi6d_5KWLnoulX1e3A?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>


# Creating Policy Templates


# Managing Policy Templates


# Asset Management

This asset management interface offers a consolidated view of assets and sub-assets showcasing important metrics such as total assets, sub-assets, and critical assets.&#x20;


# Assets

The "Assets Class" section provides detailed information on each asset, including ID, name, risk values, descriptions, and associated entities. Users can easily search, add new assets, or upload assets in bulk, making the management process more efficient.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXcrj3tPIgZBxmU4mehnUB8P96rkhidDE_RlSWeK08nXTsdEjXFgUz6ygOwI72LrB1pxOLsSHZ878G1ezmfStkdHTPWSjD-0GPIotlYb_VSv4fFejxFdEifc1XTpR3P9kFbKRfv3h-YOHWH_AnvIHhn3VkaQQaiI1NqbfWgkOw?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXeFo7jLeByItYuhDIzxiFih2DY6J2qaVmJcKkOAgObE_TSht_ABiuR2o39EMv3sRXUMMOO4Zorf5-D_RB_B3o1nv_KfYfphsRKO5_yQaBZcvIebWzOvXJbbnaQqG3InykX0kSoCN9KaYUovpOedHsOSoiWU?key=xWxaZUPob3PHzaeEfA17asEg" alt=""><figcaption></figcaption></figure>

CIA values can be assigned to assets to determine their criticality or importance.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXfGObpt4-PB-Yp8EwNqvULSL_PI8mEJQKmrAoFqQm2fXSe0s4cG9RwA30qq3wvpeNeVX8DK0ntV60TTXYx4bZFmXNV9nR1-Z1hnf1A1mPCfMVV2fGD-y-zmyDKWbBz2Yc8ktiuebarZhUXfZJndL6rv7sOK?key=xWxaZUPob3PHzaeEfA17asEg" alt=""><figcaption></figcaption></figure>

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXekQnyucJjmhVzCbrh6VPLnl5tI9888ahRDurjKCKeKUWWkhvrrcfHksVaF7u3stwTNwLfbDLc_P9mzkJEd9tDsOXMUl68TqerOxVIKItaWuMqf17LfKZ8VG_RM4uTE-t4jLRLsvGciACKN_YC_2cos4i8W?key=xWxaZUPob3PHzaeEfA17asEg" alt=""><figcaption></figcaption></figure>

Assets can be imported in bulk.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXeONAd2n8ujqbDD3kZ_iiYOBNPXySr0GKasDbFVDgrktRqLo65xNRTdt75oqGTsoXaTRjYHLjFpdmaN08b2FLFBLrBM8dVeikLujNbu-yADv4azbxohCb3Z77k6hxFJAG4NlN3qKQ3l-3ZLTs6-6qHi3MN-?key=xWxaZUPob3PHzaeEfA17asEg" alt=""><figcaption></figcaption></figure>


# Sub-assets

This environment manages sub-assets assigned to each parent asset. Similar to Assets, sub-assets can be added individually or in bulk following the Complyan template.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXc-O36Yrk15Th4z0iPuBo7T9Y9QTUTbpcF_tMErUVzuOHo6tf9QjtTnbZ14A_emYlcG61pLuRSP6wWYLiaLX_5uylKKwODFlM5OZcZ8NeWPtHKDOdCj0h5IVySz6FejBIvOFcPxUoxENXuM43BmOGjYZH_JLuBU2XJJXXgb?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXegDXPyDfJG2URFjmqGqajBfFYTcT8nqCQeiuP81poKNTNuts-nFjVVz0gFl-aexIFpGYqbzWy6gdxSTTokel2_yTYa9Q1i66ouq1s1O2_jDS9m-AqV6_nrc51vEUXwnObvWmBtgqQtdvlOejb0EG9AlW_P?key=xWxaZUPob3PHzaeEfA17asEg" alt=""><figcaption></figcaption></figure>

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXd3JI0DnDPsE8NX-QLwi_yZWRGtEfKGa1g1jdfdd9xev5bH0PKVIgTP5fQOnryS7bZmssL1O0Qh7pxur7GKuWODbeDejc3AZjddFAxfw4rNgTFioPhW-ZEvhKLDp2S3DFTGlpZ8TpoQsKQCuj59nYcOZrSr?key=xWxaZUPob3PHzaeEfA17asEg" alt=""><figcaption></figcaption></figure>


# Entities Compliance


# Understanding Entities Compliance


# Applicability and Usage


# Entities Submission


# Risk Management

**Complyan** simplifies the process of risk management by providing a centralized platform to track, assess, and manage third-party risks. The risk dashboard gives an overview of the organization's risk management status, including important data and visual breakdowns. It displays the overall number of hazards found, the status of ongoing response activities, the current degree of residual risk, and the progress of risk assessments at the top.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FcxtJbu5CwZOyVlKI6Ea4%2FHow%20to%20Manage%20Risks%20in%20Complyan%20-%20Step%200.png?alt=media&amp;token=ace259e9-ceab-4880-b411-1f2a9d2bf3d2" alt=""><figcaption></figcaption></figure>


# Risk Register

The Risk Register serves as a centralized repository to record all identified risks. It includes detailed information about risk treatment options and plans, risk matrix, level of residual risk etc. This feature allows users to systematically track and manage risks across the organization as well as track and schedule periodic assessments for the organization.

In this module, new risk can be created singly or in bulk when you click the **Actions** button.&#x20;

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FSAdiRxYY7AuEEPrP8MGX%2FHow%20to%20Manage%20Risks%20in%20Complyan%20-%20Step%2010.png?alt=media&amp;token=09a1a300-00c9-4985-a91d-3c5c3acff171" alt=""><figcaption></figcaption></figure>

Risks can be added to the register by one of the two ways shown below. Select any option and follow the steps as required.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F9NS2Bps9ZWpFkxMqzaFY%2FHow%20to%20Manage%20Risks%20in%20Complyan%20-%20Step%2011.png?alt=media&amp;token=07b313b2-bee9-4a38-9d98-150a2a2a703f" alt=""><figcaption></figcaption></figure>

Under the Configurations tab, risk assessments can be toggled on or off. Treatment of identified risks can also be configured based on specific controls.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FPSDV4ampd9P02H4ONfdF%2FHow%20to%20Manage%20Risks%20in%20Complyan%20-%20Step%208.png?alt=media&amp;token=d15645b4-ad68-4471-8677-4e8a4b516b3f" alt=""><figcaption></figcaption></figure>

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXdw_eRWj_FeeCsfHidHW01Knvi2fHTTKJMNteqgEX44Bu2PU5BD_2JE-uhsozmP3I8jPRBuPVQPrnECXcNfUlpmIud1sqjzcCt7mfsyVcE8DprufMQpmOYun3zECEVIuSFnOVPmrJ4l9wUbRMvRr0JHt0xCgyuZjyW0dRbomQ?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>


# Mitigation Planning

The Risk Mitigation interface is designed to help users track and manage mitigation plans and their corresponding approvals for risks within the organization. The dashboard offers a real-time overview of the current state of mitigation efforts, categorized into the following areas:

1. Closed: Displays the total number of mitigation plans that have been successfully completed and closed.
2. Mitigation Rejected: Shows the number of mitigation plans that were reviewed and rejected.
3. Mitigation In Progress: Displays the count of mitigation plans currently being worked on.
4. Approval Pending: Lists the number of mitigation plans that are awaiting management approval.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXf2kPP60JJothCAUMOoFRiDYCtZBw0gHfvXYLlwsAdT7TZ3w-3_xnLLYNSVJuaqjhVplj7JR_wGvobFABocogymDUeNPzCmzCDaJEIZAMX0z_x3H_qhaZc53daU9cSxLTyRK1XPaE-rocLZC9zSGd-XSGfWMfS48WhdTnpWAw?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>


# Risk Matrix

The Risk Matrix interface allows users to visualize and assess risks based on their likelihood and impact. It is used to log and determine the severity of various risks and helps prioritize risk mitigation strategies. The key components of this section are:

**Select Matrix Type:**

* This feature allows users to select the size of the matrix grid based on the complexity of their risk analysis. The available options are:
  * 3x3 (default)
  * 4x4
  * 5x5
* Users can select the matrix type from the dropdown menu and click the Update button to apply the selected configuration. The matrix will adjust accordingly to reflect the chosen grid size.

**Risk Matrix Display:**

* The matrix is displayed as a color-coded grid that categorizes risks based on their Impact (y-axis) and Likelihood (x-axis):
  * Impact ranges from Low to High, while
  * Likelihood ranges from Rare to Likely.
* Each cell within the matrix represents a combination of impact and likelihood, color-coded to reflect the risk level:
  * Green: Low risk
  * Orange/Yellow: Medium risk
  * Red: High risk

**Risk Categories:**

* Users can manually adjust the risk levels (e.g., Low, Medium, High) for each combination of impact and likelihood by using the dropdowns in each matrix cell. This enables customization based on the organization’s risk tolerance and specific scenarios.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXe-KXQso_IUPv0AU6rV8nP5DB7NBsSdP_-Ptkmaom2_PxEgdhen6gQHp_mlPS5xPYTAnPelebNeQt3ddyoOZFdPkE7uAS4RWF0C9Q8BhfpQ49WG_BPZlpN1eqm5HGtBoqFzHQwWC10z2qLDb48dpmBk3vZgwSpfiFBONHyO?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXfhPVoZyTCBawwLodPlgEEp35xXPzftQQBQSoVexTETfcjWuvMs2k_DlmWA9rlG2Cu_ARMOPxfgXy13VgPE32umaTVFf9Fs7P_AeEwPN3k9fBHkyK5FlS7jsjbdJrXG-rFy1hlv6p6crc8TMPbO9zp-RUAvxcNZ1lPxK9uHtg?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>


# Risk & Threat Catalog

This section provides a structured interface where users can view, categorize, and manage organizational risks and threats. The catalog is split into two tabs: Risk and Threat, allowing users to toggle between risk and threat management. The default display shows a list of the organization’s risk with the following features:

1. Risk ID: A unique identifier for each risk in the system.
2. Risk Event: The specific event or condition that may present a risk to the organization (e.g., Incident Response, Business Continuity).
3. Description: A brief explanation of the risk event and its implications.
4. Function: This section indicates the functional area of the organization responsible for managing or mitigating the risk.
5. Actions: Provides action buttons for managing each risk entry. Actions may include options to expand or collapse details, edit, or delete the risk.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXcAhGsfvXUyvYtrL1YjntwsqVm1Qj4P5ajWxTENMGGUvCPqn6VascRcAV8UFNjpkQlu96eCEgdOzqyni7cuYA2U7RqSX6oIAIGVxHmUWizd2X_o_s_8jkRVcpSB1B4CHh5Rr33fZNMKPXJwAcGgvnBTL4By3VjQEWbcsdp3nw?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXeeJKXRl16VzKZCSR4Cjpd398TAt9nnvF8gKiUEvapViQX-8mVS9tCk5mH48NbCfv_X2coXiN4LGCyWNb71PW1evhLOYWft9AHbda_xPxnGXar_RVWrworKUlT22lZN2aH6hgSeI4YEOcdS6ejgWmIcVNSgPbXZau9dw1A?key=wWjbrBi-D3VKs2iDr_CXHUKd" alt=""><figcaption></figcaption></figure>

**New Risk(s) can be created here.**

* Users can click the New Risk button located on the top-right corner of the catalog. This will open a form to create a new risk entry.

Create Risk Form:

* The Create Risk form allows users to input essential details about the risk, which include:
  * Risk Grouping: A dropdown menu to select the category or group the risk belongs to.
  * Risk Name: The name of the specific risk event.
  * Risk Event: Further details of the risk event being added.
  * Description: A detailed description of the risk, outlining its potential impact and relevance.
  * Function: Select the department or function within the organization that is responsible for managing this risk.

Create Button:

* After filling in the required fields, users can click the Create button to new risks to the catalog. The risk will then appear in the list, ready for monitoring and management.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXdorngrcLgzyP46NlS_vAwUUVCSrsJ7yMDZ-VIMRSEYQphFUaydDy6kS0M82XdClHIX6VcmGlz7AFgiKW59hg5gvp5lwI_E__VmeAusYI8PqFwa1rAFv0bsf_ay_NVjAFDkLbXuoByO9JK9tLwnvEaZTbfTcXtU_ylLwOrP?key=NKP5tXXWqw35BZZky8hVoN_P" alt=""><figcaption></figcaption></figure>


# Data Processing Register


# Assets


# Creating New Assets and Sub Assets


# Managing Assets and Sub-Assets


# Data Processing Activities


# Reports and Dashboard


# Assignments


# Data Protection Impact Assessment


# Exploring The DPIA Dashboard


# Process and Implementation


# DPIA Reports


# Managing DPIA Assignments


# Third-party Risk Management

Third-party risk management (TPRM) is essential for managing risks from external partners. **Complyan** simplifies this by providing a centralized platform to track, assess, and manage third-party risks.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FB9n9R1okiu50UDn8CZxw%2Fimage.png?alt=media&amp;token=86f8aa49-83b7-483c-8ae7-93c9b4b2ac51" alt=""><figcaption></figcaption></figure>


# Suppliers

Suppliers form a critical component of the organization’s Governance, Risk, and Compliance (GRC) framework, as they directly influence the integrity, security, and resilience of business operations. By engaging with suppliers, an organization extends its ecosystem, which means supplier practices in areas such as cybersecurity, data protection, ethics, and regulatory adherence must align with the organization’s own policies and compliance obligations. Risks introduced through suppliers, whether cyber incidents, operational failures, or legal non-compliance, can significantly impact organizational performance and reputation. To manage this, the organization must implement structured supplier governance processes that include due diligence, risk assessments, continuous monitoring, and clear contractual obligations to ensure accountability. Complyan supports this by providing an integrated Third-Party Risk Management (TPRM) module that automates supplier onboarding and monitoring of their compliance with your organization.

In this section, suppliers can be added by using the available options. This dashboard can also be exported.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FRBOkrz8a6QwNlRqD5hEd%2FManage%20Suppliers%20and%20Questionnaires%20-%20Step%207.png?alt=media&amp;token=27c3d03e-fdeb-43cf-88dc-cfc429f0f794" alt=""><figcaption></figcaption></figure>

Using the **Invite Supplier** option, you may select the **Send Onboarding Questionnaire** to the invitees at the same time.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FfsKfvIZdyxVXzpzfM1l5%2FManage%20Suppliers%20and%20Questionnaires%20-%20Step%208.png?alt=media&amp;token=b3110791-e4e0-4847-ae8f-5644c150dcec" alt=""><figcaption></figcaption></figure>

The **Search** options can be used to filter and categorize suppliers.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F2S5O3TYBTitkMV5WzrFV%2FManage%20Suppliers%20and%20Questionnaires%20-%20Step%2028.png?alt=media&amp;token=4cf58948-b32a-4ba8-9596-5f7565f42daf" alt=""><figcaption></figcaption></figure>


# Supplier Assessment

This section allows the sending of questionnaires if they were not sent during the invitation process.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2Fkxog91S8zILznYNORL3N%2FManage%20Suppliers%20and%20Questionnaires%20-%20Step%2035.png?alt=media&amp;token=cf4dd903-13f6-4897-a6f2-e23d2082c74a" alt=""><figcaption></figcaption></figure>

Follow the steps until a questionnaire suitable for the **Vendor** or **Entity** has been created.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FpKMRIcn8Wy9yhCBeBlBq%2FManage%20Suppliers%20and%20Questionnaires%20-%20Step%2039.png?alt=media&amp;token=bb1f7251-c3dc-4baa-b92c-faf1a9bf727c" alt=""><figcaption></figcaption></figure>


# Questionnaire Templates

In this tab, templates are configured and narrowed down to specific areas of security and to fit into different supplier/vendor type.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FysHv9NSxg7i5ACXzxOdw%2FManage%20Suppliers%20and%20Questionnaires%20-%20Step%2044.png?alt=media&amp;token=7db6d1b2-0177-4976-9050-f9957107a949" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FNTrJ3QLuynl2B1qOMJh2%2FManage%20Suppliers%20and%20Questionnaires%20-%20Step%2045%20(1).png?alt=media&amp;token=4d422d8e-e57a-45be-9e22-2e40709baeb1" alt=""><figcaption></figcaption></figure>


# Documents

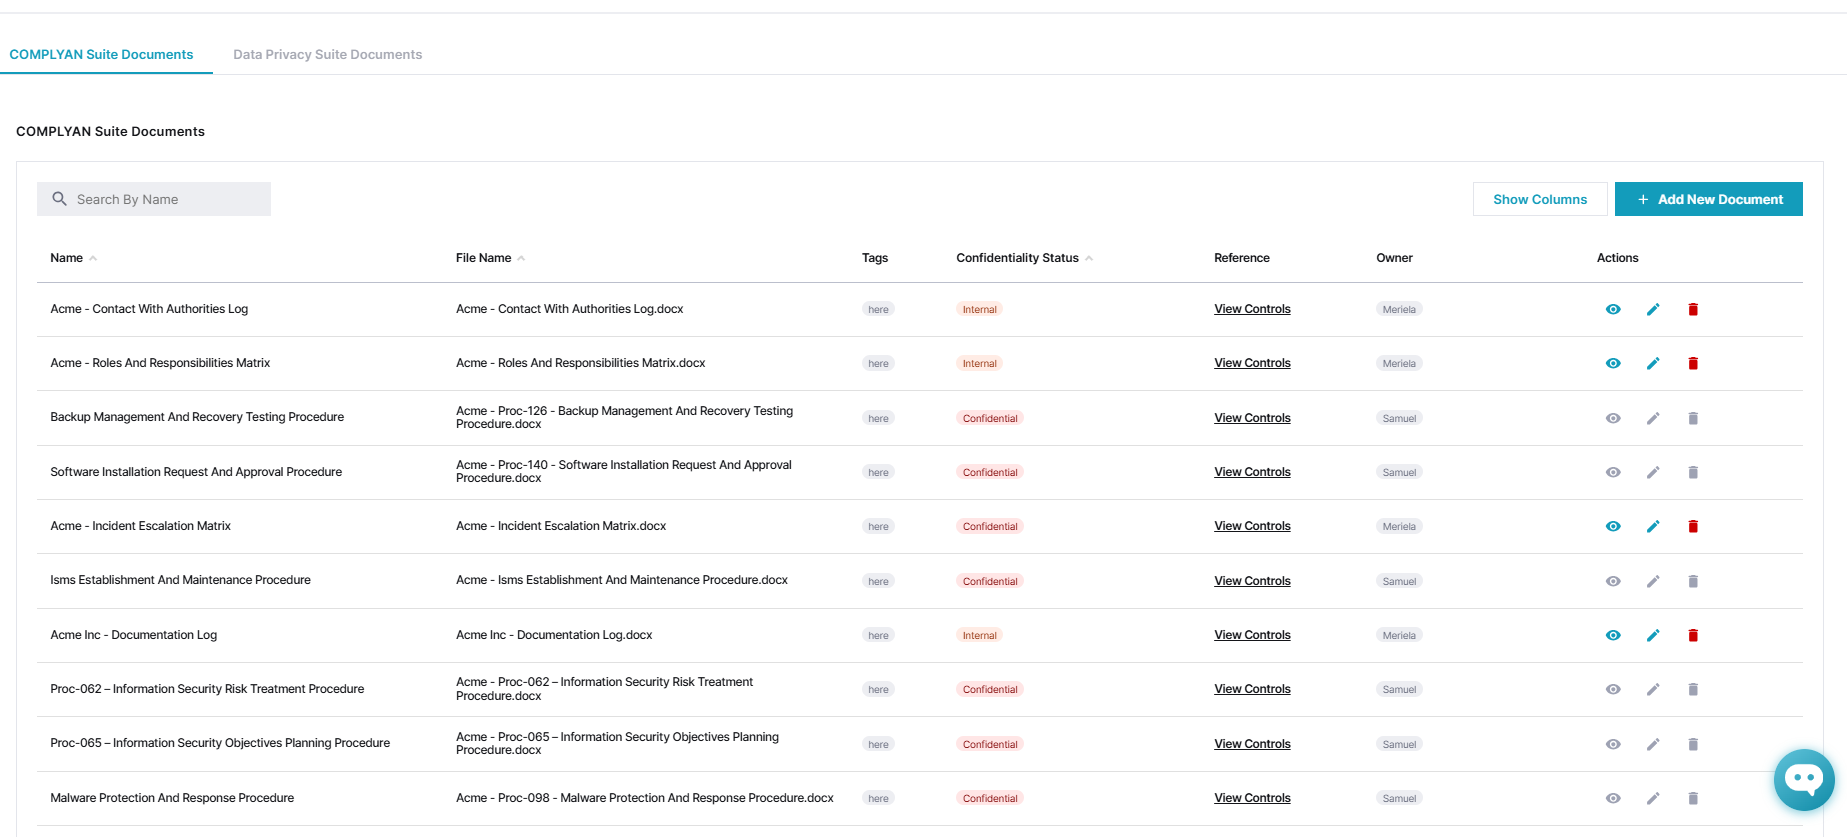
This Document Inventory page serves a repository for all documents attached as evidence during framework implementation.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FNmfoBdVxewFLUmv1t1uA%2Fimage.png?alt=media&amp;token=294a17c2-5ad7-4935-ad66-2221abc98a0a" alt=""><figcaption></figcaption></figure>


# User Management

The Users Management section provides administrative control over the organization's user accounts and roles. &#x20;

<br>


# Users

Within this section, the **Member Users** tab allows administrators to add new users, view, manage, and edit individual user profiles.&#x20;

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FlUEH9V5sYmu3rQtj4ZfM%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%209.png?alt=media&amp;token=27f011a1-d1da-4f58-a481-806bf0355d81" alt=""><figcaption></figcaption></figure>

The **Guest Users** tab can be used to temporarily grant access to third-parties on the platfrom.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F55eUJ202pGVw95C7Kfef%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%205.png?alt=media&amp;token=b300bedf-fbec-409d-b6b7-a6ff5c3bb244" alt=""><figcaption></figcaption></figure>


# Roles

The Roles tab offers a way to define and manage role-based permissions for groups of users, ensuring that each user has appropriate access based on their job responsibilities.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXdMwwQDHcPG_6feTDF9VVipZT-47MQPq6BpJEvjP7WgLno_12atw2NMaYSkXL-XP8jO940HmHG4KhLkTYL_665eaLvZnuxU-zrae5143tMnnC-zwYcEX0D05CFwYWPcvngMk0NhQA2KmwfyVMr633X_QrKl_Z1PjXwXcv2i7Q?key=xWxaZUPob3PHzaeEfA17asEg" alt=""><figcaption></figcaption></figure>

New roles can be created with permissions assigned to each role and subsequently assigned to users upon their creation.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXcaA00aKLzrq48p1C6hkBiwkYR6fIb10dvv4kUxUbUFYeKmyfPN2SChy-jH8qAEoAlCThzHvQ2rUCb4QRFSii2z8ZbPbmziLqvhC3JoWNka3gC51DzcbeZ86ycXLRNUhyN0bQLqHSj4pOR2CsXXpagQZUW8j7KtzVnYBbzL?key=xWxaZUPob3PHzaeEfA17asEg" alt=""><figcaption></figcaption></figure>


# Integrations

This module provides synchronization between Complyan and enterprise tools and services.

Available services are visible in this view.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FU9elddBt9UiNS7Bo3D3g%2Fimage.png?alt=media&amp;token=d8366d83-a353-4613-85d3-3d91e3eceaa2" alt=""><figcaption></figcaption></figure>

Use **Details** to understand each service and proceed to **Connect.** For instance, to integrate Amazon Web Services (AWS):

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FNGzhYwNaeZCUtR2lf4JS%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2020.png?alt=media&amp;token=711b016e-ea95-4dcf-9ef5-b027b2aa2adc" alt=""><figcaption></figcaption></figure>

This will reveal lists of supported tests and control for AWS integration.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FdzIoVlnhpScqNTMPFuEm%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2021.png?alt=media&amp;token=142f4be4-2d62-430f-b23d-061972bb54aa" alt=""><figcaption></figcaption></figure>

Select **Connect**.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FfObBa4Ov9XicTJ0RQZWo%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2024.png?alt=media&amp;token=43d907f9-7ec2-4857-b188-7918d2eaa2b0" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FvrRDo53IDdGacyX93dDW%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2025.png?alt=media&amp;token=f0abe113-721c-4c62-9cd0-2d5c444f6abc" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FOB6iIOYK7N0fLUIBVjdL%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2026.png?alt=media&amp;token=3f6dfba2-42a2-4f68-b07d-a5fd2a84be44" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FvvLfMx0A8faLtwNjzZoL%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2027.png?alt=media&amp;token=28d74a80-7cd1-4d07-b566-08a70705b3e4" alt=""><figcaption></figcaption></figure>

Follow the prompts as described until succesful.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FHYUHAOz27JWjYNfare8Z%2Fimage.png?alt=media&amp;token=fee77788-9f84-4d0c-bde5-f566a3469ae6" alt=""><figcaption></figcaption></figure>


# Manage

This module is used to manage various aspects of your integration from the Integration section.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FNLwqOFuWnll3oxUEt2kY%2Fimage.png?alt=media&amp;token=059adba9-a366-4788-bba0-2104e6bb94ef" alt=""><figcaption></figcaption></figure>


# People

This section contains management options for users in your Active Directory. It also provides the capability to create users manually even if the AD is not connected.

Use **Notify** to send an email notification to users to follow Checklist items (see next page).

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FtWUT4adBShJ5H8EeWA6R%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2035.png?alt=media&amp;token=c7e63da8-a6a0-4a70-8078-172bbae157c9" alt=""><figcaption></figcaption></figure>


# Groups

This section is used to group **People** based on their organizational roles. This helps to facilitate training, checklist and management efforts.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2F9yRRG3c4unZYOLuRHtRD%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2043.png?alt=media&amp;token=38a9a1aa-a513-4754-8435-1120f4d6ff36" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FAOg4lSw2ITx91hkfPS3n%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2044.png?alt=media&amp;token=fe0bbd3c-99db-4744-a375-1735459a9b72" alt=""><figcaption></figcaption></figure>


# Checklist

This section lets an administrator build a tailored compliance checklist that ensures that the **People** of the organization go through the necessary policy sign-offs, training, and contract agreements before being considered compliant.

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FWJ2ca9spfZQGsxaMLwSm%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2048.png?alt=media&amp;token=e98572fa-e8f9-48cc-90a0-33230df85a1a" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FrASZyLEyzyB3M4fIEtSu%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2049.png?alt=media&amp;token=013ccdcc-8ca7-4fb7-a352-1f71fd5756e6" alt=""><figcaption></figcaption></figure>


# Trainings

In this section, training programs can be created to ensure awareness, enlightenment and compliance among the **People,**

<figure><img src="https://3772445253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F9LO57DuBVSAuEHl27p2k%2Fuploads%2FgVBLErgken07W5Sp8xew%2FHow%20to%20Navigate%20and%20Manage%20Complyan%20Features%20-%20Step%2054.png?alt=media&amp;token=3b98f58a-a164-4b3f-b235-3973a638f696" alt=""><figcaption></figcaption></figure>


# Administrative Settings


# Configurations, Preferences and Customizations


# Account Security Settings


# Adding Compliance Farmeworks


# Managing Entities and Custom Fields


# Cross Mapping


# Audit Logs


# Accessing and Understanding Logs


# Meetings and Follow-ups

This environment is used for collaboration and synchronization across teams. It is also used to log personal tasks.

1. Select “Create Event” to either schedule a call or log a personal task.

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXexjQ04-9sIqc6eCx0yzMTN_QkR-1IeAVNwF4gF563q6LtGm6iDR5nFbk3Ma1hOlBNxnUVs5Xa44Tl6RVE3Z3hfZWq3IDTL32ta_K6Mhi2ZB8azp11ogPdVTYzgnrrrkWstk4TlYiknzn-dF6PkEwD-Pz_ck5JRTHxX1pA6?key=NKP5tXXWqw35BZZky8hVoN_P" alt=""><figcaption></figcaption></figure>

<br>

<figure><img src="https://lh7-rt.googleusercontent.com/docsz/AD_4nXfF-Tpx-ow97Hrl52Da7tqvFVSf8eoc11XJGufCp0HRzD2GIzHhYfpKgrVUFYlyeprBr7pmQuqF4sAowuYckC2L8Gx6nAbsbD3T7Fbmjr-40_BdlS5Bk2qwuxfY6gvvhozPdEy-RATuPto_KmBtULur1txPCaUMsziyimZLzw?key=NKP5tXXWqw35BZZky8hVoN_P" alt=""><figcaption></figcaption></figure>


# Appendix


# Glossary of Terms


# Frequently Asked Questions (FAQs)


# Additional Resources